0click enterprise compromise - thank you, AI!
Security researchers examine technical aspects of 0click enterprise compromise - thank you, AI!.
Summary
Overview: Compromising a well-protected enterprise used to require careful planning, proper resources, and ability to execute. Not anymore! Enter AI.
From Initial Access to Impact and Exfiltration. AI is happy to oblige the attacker. In this talk we will demonstrate access-to-impact AI vulnerability chains in most flagship enterprise AI assistants: ChatGPT, Gemini, Copilot, Einstein, and their custom agent . Some require one bad click by the victim, others work with no user interaction – 0click attacks.
Compromising a well-protected enterprise used to require careful planning, proper resources, and ab Details: ility to execute. Not anymore! Enter AI.
Initial access? AI is happy to let you operate on its users’ behalf. Persistence? Self-replicate through corp docs. Data harvesting? AI is the ultimate data hoarder. Exfil? Just render an image. Impact? So many tools at your disposal. There's more. You can do all this as an external attacker. No credentials required, no phishing, no social engineering, no human-in-the-loop. In-and-out with a single prompt.
Last year at BHUSA we demonstrated the first real-world exploitation of AI vulnerabilities impacting enterprises, living off Microsoft Copilot. A lot has changed in the AI space since... for the worse. AI assistants have morphed into agents. They read your search history, emails and chat messages. They wield tools that can manipulate the enterpr
Related talks

Microsoft Security Response Center (MSRC)·32 min
Presenters detail vulnerability discovery and exploitation in BlueHat 2026: 0click enterprise compromise.
OWASP Foundation·17 min
Engineers explore architecture and security mechanisms for OSINT to Compromise Frank Vianzon.
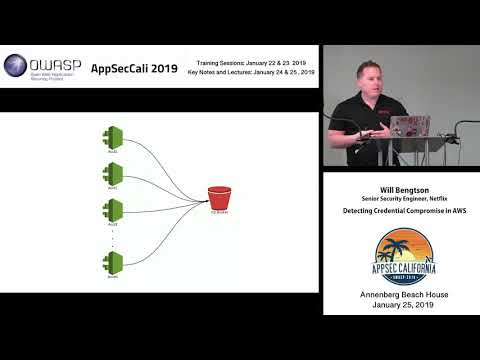
OWASP Foundation·48 min
Will Bengtson
Will Bengtson examines AppSecCali 2019 - Detecting Credential Compromise in AWS.