Backdooring the Frontdoor
Jmaxxz audits leading smart door lock systems, demonstrating authentication bypasses and physical lock opening via unencrypted BLE telemetry.
Summary
Architecture and Background
As our homes become smarter and more connected we come up with new ways of reasoning about our privacy and security. Vendors promise security, but provide little technical information to back up their claims.
Vulnerability Analysis
Further complicating the matter, many of these devices are closed systems which can be difficult to assess. This talk will explore the validity of claims made by one smart lock manufacturer about the security of their product.
Exploitation and Demonstrations
The entire solution will be deconstructed and examined all the way from web services to the lock itself. By exploiting multiple vulnerabilities Jmaxxz will demonstrate not only how to backdoor a front door, but also how to utilize these same techniques to protect your privacy.
Remediation and Defensive Strategies
Jmaxxz works as a software engineer for a Fortune 100 company, and is a security researcher for pleasure. His FlashHacker program was featured in Lifehacker’s most popular free downloads of 2010. More recently he has contributed to the node_pcap project which allows interfacing with libpcap from node. His other interests include lock picking and taking things apart.
Related talks

Main Stage·42 min
Mark Omo · James Rowley
Reverse engineers electronic gun safes and commercial digital vaults, demonstrating effortless physical and electromagnetic bypasses across leading brands.
Main Stage·40 min
Dennis Giese · braelynn
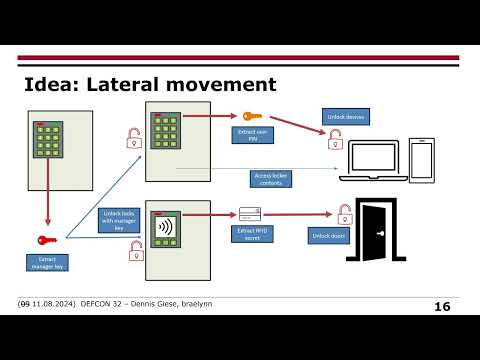
Security evaluation and hardware attack surface analysis of smart electronic lockers and storage cabinets.

Main Stage·20 min
Michael Orlitzky
Hardware vulnerabilities and bypasses in smart, app-controlled commercial laundry machines and payment mechanisms.