Dissecting a Ransomware Operation: From Propagation to extortion
Discusses dissecting a Ransomware Operation: From Propagation to extortion and evaluates key implications for security practitioners.
Summary
Ransomware evolution
A Rootcon speaker traces ransomware from Joseph Popp's 1989 AIDS Trojan floppy targeting WHO attendees—symmetric encryption and Panama bank payments easily reversed—to today's epidemic fueled by cryptocurrency, global connectivity, and strong public-key cryptography.
Ransomware-as-a-Service
Modern operators sell builders and affiliate programs with monthly subscriptions near forty dollars or eighty-twenty profit splits, providing encryptors, decryptors, negotiation infrastructure, and customizable payloads while affiliates conduct attacks.
Attack chain
Affiliates still rely heavily on phishing, including HR-themed resume attachments with nested archives, exploiting non-technical departments. A Vietnam livestreamer case shows attackers impersonating Black Myth: Wukong developers to deliver malware during a broadcast. The talk covers affiliate onboarding, builder customization, and common initial access vectors preceding encryption.
Related talks

Videos·42 min
Raul Alvarez
Raul Alvarez analyzes Insomni'hack 2017 - Dissecting a Metamorphic File-Infecting Ransomware.

Black Hat·36 min
Security researchers examine technical aspects of It's not FINished: The Evolving Maturity in Ransomware Operations.
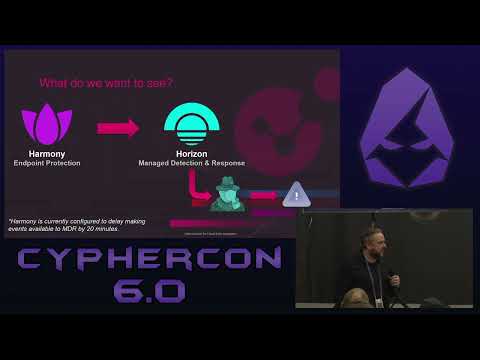
Hackers of CypherCon·27 min
Checkpoint | CypherCon 6.0
Checkpoint | CypherCon 6.0 investigates Operation BORDERLAND Ransomware vs. Horizon MDR.