Global AppSec Dublin: A Taste Of Privacy Threat Modeling by Kim Wuyts
Analyzes global AppSec Dublin: A Taste Of Privacy Threat Modeling by Kim Wuyts and evaluates key implications for security practitioners.
Summary
Overview: Kim Wuyts presents at OWASP Global AppSec Dublin on privacy threat modeling, using an ice-cream metaphor to introduce data minimization before diving into technical methodology.
Key Topics: Why privacy matters alongside security in digital transformation; common misconceptions about privacy in the security community; the why/what/how framework for privacy analysis; and integrating privacy into threat modeling workflows.
Technical Details: Wuyts advocates collecting only necessary personal data, paralleling parental wisdom about not ordering every ice cream flavor. She demonstrates how privacy threat modeling extends traditional security models to address data protection and regulatory compliance.
Takeaways: Privacy and security are complementary disciplines. Practitioners should adopt data minimization as a default principle and incorporate privacy-specific threats into existing threat modeling practices.
Related talks

OWASP Global AppSec Dublin·58 min
Izar Tarandach
Analyzes global AppSec Dublin: Threat Modeling In And For Your Organization and evaluates key implications for security practitioners.

OWASP Foundation·43 min
Seba Deleersnyder
Seba Deleersnyder analyzes Designing Security And Privacy: A Dev's Guide To Threat Modeling With OWASP SAMM.
OWASP Foundation·41 min
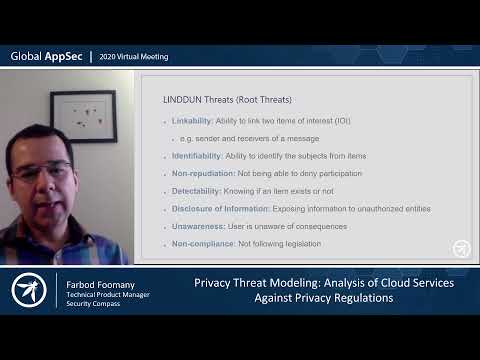
Security researchers examine technical aspects of Privacy Threat Modeling Analysis of Cloud Services Against Privacy Regulations Farbod H Foomany.