Hidden Attack Surface of OEM IoT Devices: Zero-Click RCE in Top Routers
Octavio Gianatiempo and Octavio Galland audit top-selling consumer routers, discovering systemic OEM firmware vulnerabilities that enable zero-click remote RCE.
Summary
The Fragmented World of OEM Firmware Supply Chains
Many consumer networking brands rebrand hardware and firmware from Original Equipment Manufacturers (OEMs), propagating legacy vulnerabilities across dozens of distinct products.
Reverse Engineering Embedded Router Firmware
Octavio Gianatiempo and Octavio Galland audit best-selling SOHO routers, analyzing closed-source MIPS binaries, proprietary UPnP handlers, and web daemons.
Discovering Zero-Click Remote Code Execution Vulnerabilities
The researchers demonstrate exploiting unauthenticated stack buffer overflows in network management daemons to gain root shell access remotely.
Securing the Embedded Device Ecosystem
The presentation discusses vendor disclosure challenges with white-label manufacturers and provides hardening recommendations for consumers and ISPs.
Related talks

Main Stage·40 min
Reynaldo · nyx
Reverse engineers commercial vape and sound monitoring sensors installed in school restrooms, uncovering unauthenticated telemetry feeds and cloud vulnerabilities.

Main Stage·42 min
Mark Omo · James Rowley
Reverse engineers electronic gun safes and commercial digital vaults, demonstrating effortless physical and electromagnetic bypasses across leading brands.
Main Stage·40 min
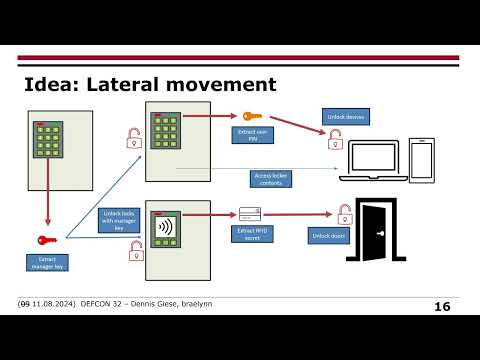
Dennis Giese · braelynn
Security evaluation and hardware attack surface analysis of smart electronic lockers and storage cabinets.