Stargate: Pivoting Through VNC
Yonathan Klijnsma and Dan Tentler present Stargate, a framework for weaponizing exposed VNC endpoints as encrypted pivoting tunnels into private enterprise networks.
Summary
Architecture and Background
VNC is a great tool to use if you need to get to a box you're not physically near. The trouble with VNC is that it was invented 15+ years ago and hasn't been improved upon in any significant way. Besides the internet of things being sprinkled with VNC endpoints, there are companies which use VNC to such a large degree they need a VNC proxy on their perimeter to get to all the internal VNC hosts - some of which are ICS/SCADA devices.
Vulnerability Analysis
Stargate is the result of discovering a vulnerability in these VNC proxies that allows you to proxy basically anything. This allows you to do anything from using them as anonymous proxies, conduct reflective scanning, pivoting into the internal network behind it, and more. In this presentation we will show you exactly what Stargate is, how we encountered it, the 'fun' things you can do with the Stargates all around the globe and we will release the Stargate tool which anyone can use to talk to/through these devices.
Exploitation and Demonstrations
Bios: Yonathan Klijnsma is a senior threat intelligence analyst working for Fox-IT, a Dutch IT security company. Yonathan specializes in the analysis and tracking of attack campaigns, work out the attacker profiles and investigate the techniques and tools used by attackers. Yonathan's area of focus lies in the espionage related cases.
Remediation and Defensive Strategies
Outside of work Yonathan likes taking things apart and figuring out how they work; be it physical devices or digital like malware or ransomware. Occasionally a write-up of one of these projects ends up on his personal blog. Dan Tentler is the founder and CEO of The Phobos Group, a boutique information security services company. Previously a co-founder of Carbon Dynamics, and a security freelancer under the Aten Labs moniker, Dan has found himself in a wide array of different environments, ranging from blue team, to red team, to purple team, to ‘evil hacker for a camera crew’. When not obtaining shells or explaining against how to get shelled, Dan enjoys FPV racing, homebrewing, and internet troublemaking.
Related talks
Red Team Village·51 min
Evan Anderson
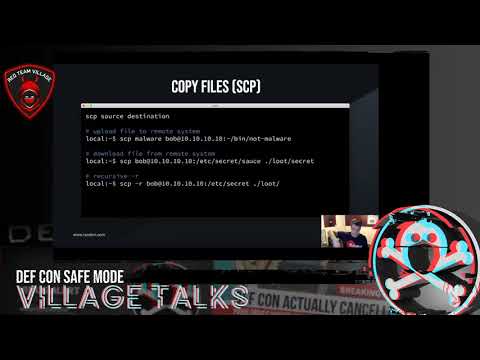
Evan Anderson explores advanced SSH tunneling techniques, local/remote port forwarding, SOCKS proxies, and stealthy lateral movement strategies.

Main Stage·35 min
Justin Perdok
Justin Perdok exploits User-ID mapping features in Palo Alto and SonicWall enterprise firewalls, spoofing domain identities to bypass network segmentation rules.

Main Stage·24 min
droogie
Revives Windows null session attacks against modern Active Directory environments, demonstrating significant unauthenticated enumeration capabilities.