Web Application Analysis with Owasp Hatkit
Holst Swende and and Karlsson explores web application analysis with owasp hatkit at DEF CON 19, examining database-security and practical defenses.
Summary
Architecture and Background
Martin Holst Swende, Patrik Karlsson - Web Application Analysis With Owasp Hatkit The presentation will take a deep dive into two newly released Owasp tools; the Owasp Hatkit Proxy and the Owasp Hatkit Datafiddler. The name Hatkit is an acronym (of sorts) for Http Analysis Toolkit and are tools mainly for people who analyse (hack!) web applications.
Vulnerability Analysis
The tools make extensive use of MongoDB, in particular the advanced querying facilities in available in this database. Prior knowledge of Javascript and Python is an advantage, but absolutely no requirement.
Exploitation and Demonstrations
Martin Holst Swende is a Senior Security Consultant at 2Secure AB, working with application security- and penetration testing. Martin has a background as a Java/J2me-programmer but nowadays finds more joy in Python and Javascript.
Remediation and Defensive Strategies
Martin is project leader for the Owasp Hatkit Proxy/Datafiddler projects and contributor to open source security projects such as Webscarab and Nmap. Twitter: @mhswende Patrik Karlsson is a Senior Security Expert with over ten years of experience in the field of IT- and Information Security. Patrik's area of expertise includes security penetration testing, vulnerability assessments, software application security audits and incident investigations. Patrik is an active Nmap contributer and runs the security related web site www.cqure.net. Twitter: @nevdull77
Related talks
Main Stage·38 min
Abstrct
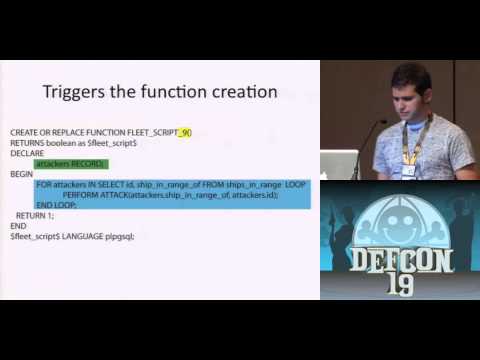
Abstrct - When Space Elephants Attack: A DEFCON Challenge for Database Geeks The Schemaverse is a vast universe found purely within a PostgreSQL database.
Main Stage·38 min
Alexander Kornbrust
Alexander Kornbrust explores hacking and securing db2 luw databases at DEF CON 19, examining database-security and practical defenses.

Main Stage·47 min
David Litchfield
David Litchfield - Hacking and Forensicating an Oracle Database Server David Litchfield is recognized as one of the world's leading authorities on database security.