XiaoHuiHui - All the 4G Modules Could Be Hacked
Discovers systemic vulnerabilities across 4G LTE modem modules from major manufacturers used in billions of IoT devices.
Summary
4G Module Vulnerability Research
XiaoHuiHui (security researcher, 360 IoT Security Research Lab) presents research discovering systemic security vulnerabilities across multiple 4G LTE modem modules from major manufacturers — Qualcomm, Quectel, SIMCom, and Sierra Wireless — embedded in billions of IoT devices.
Attack Surface Analysis
4G modules expose multiple interfaces: AT commands over UART/USB, embedded web management pages, and carrier-specific OTA update mechanisms. The modules typically run embedded Linux with the modem firmware, with full network connectivity to the cellular network.
Vulnerabilities Across Vendors
Research reveals common vulnerability classes across all tested vendors: command injection via AT command interfaces, unauthenticated web management interfaces accessible from the cellular network, and OTA update mechanisms without cryptographic signature verification.
Impact Scope
The affected modules power industrial IoT deployments (smart meters, fleet tracking, industrial sensors), connected vehicles (OBD-II adapters, infotainment), medical devices, and smart infrastructure. Exploiting carrier-accessible vulnerabilities enables mass compromise of entire device categories without physical access.
Related talks

Main Stage·40 min
Reynaldo · nyx
Reverse engineers commercial vape and sound monitoring sensors installed in school restrooms, uncovering unauthenticated telemetry feeds and cloud vulnerabilities.

Main Stage·42 min
Mark Omo · James Rowley
Reverse engineers electronic gun safes and commercial digital vaults, demonstrating effortless physical and electromagnetic bypasses across leading brands.
Main Stage·40 min
Dennis Giese · braelynn
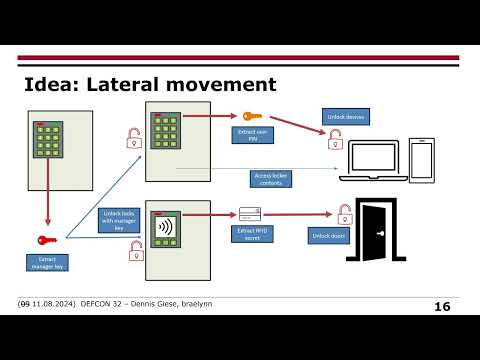
Security evaluation and hardware attack surface analysis of smart electronic lockers and storage cabinets.