CSIT Village·18 min
Theodore Lee
Theodore Lee examines reverse engineering (RE) is time consuming and resource intensive.
malware-analysisreverse-engineeringbinary-analysis+1
11 talks tagged with this topic.
Loading filters…
1–11 of 11 talks · loading…
CSIT Village·18 min
Theodore Lee
Theodore Lee examines reverse engineering (RE) is time consuming and resource intensive.
CSIT Village·20 min
Kan Onn Kit
Kan Onn Kit examines in stripped binaries, malware analysts often struggle in a sea of raw offsets and pointer arithmetic.
Black Hat·50 min
Industry experts analyze emerging threats surrounding Decompiler Internals: Microcode.
IEEE Symposium on Security and Privacy·25 min
Analysts investigate attack surfaces and defenses concerning Helping Johnny to Analyze Malware: A Usability-Optimized Decompiler and Malware Analysis User Study.
Videos·28 min
Georgy Kucherin (Kaspersky)
Outlines deobfuscating virtualized malware using Hex Rays Decompiler and evaluates key implications for security practitioners.
Videos·38 min
Igor Kirillov
Igor Kirillov examines Maximize the power of hex-rays decompiler.
Black Hat Asia·41 min
Rocky Bernstein
Security researchers examine technical aspects of How to Get the Most Out of the Python Decompilers Uncompyle6 and Decompyle3.
Hack In The Box Security Conference·36 min
Dominic Couture
Dominic Couture analyzes #HITB2023HKT D1T1 - Writing A New Decompiler Just For A Security Audit.
Hack In The Box Security Conference·52 min
Carlos Garcia Prado · Ryan Warns
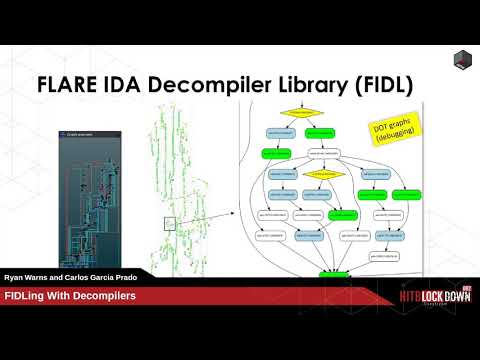
Carlos Garcia Prado explores #HITBLockdown002 D1T1 - FIDLing with Decompilers.
Recon Conference·39 min
Engineers explore architecture and security mechanisms for Recon 2018 Montreal An Open-Source Machine-Code Decompiler by Marek Milkovič and Peter Matula.
Recon Conference·1 hr 13 min
Engineers explore architecture and security mechanisms for Recon Brussels 2018 - Decompiler internals: microcode.