botconf eu·39 min
Tom Ueltschi
Tom Ueltschi analyzes Advanced Incident Detection and Threat Hunting using Sysmon and Splunk.
threat-huntingdetectionsplunk
13 talks tagged with this topic.
Loading filters…
1–13 of 13 talks · loading…
botconf eu·39 min
Tom Ueltschi
Tom Ueltschi analyzes Advanced Incident Detection and Threat Hunting using Sysmon and Splunk.
CornCon·51 min
Douglas Brush
Analysts investigate attack surfaces and defenses concerning CC7 D02 T02 Douglas Brush, Splunk, An Honest Talk About Mental Health.
Eye on Tech·9 min
Industry experts analyze emerging threats surrounding Insights from Cisco Live 2024: Splunk, ThousandEyes, Observability, and More.
Eye on Tech·18 min
Engineers explore architecture and security mechanisms for IT Ops Query: Splunk exec on AI observability's "double-edged sword".
Eye on Tech·16 min
Patrick Lin from Splunk
Analysts investigate attack surfaces and defenses concerning Splunk exec on AI observability's "double-edged sword".
PROIDEA Events·23 min
Industry experts analyze emerging threats surrounding CONFidence 2018: Splunk - bezpieczeństwo pracy użytkowników w Office 365 (Jakub Goral).
Videos·47 min
Analysts investigate attack surfaces and defenses concerning AttackIQ + Splunk SIEM Integration.
RSAC Cybersecurity·20 min
Security researchers examine technical aspects of The Future of Threat Detection and Response | Mike Horn, Splunk & Tom Gillis, Cisco | RSAC 2025.
BSides Knoxville·38 min
Ryan Hays
Ryan Hays - Weaponizing Splunk: Using Blue Team Tools for Evil.
BSidesCharm·22 min
Ryan Hays
2017 - Ryan Hays - Weaponizing Splunk: Using Blue Teams for Evil.
Zero Day Con·20 min
Mark Woods
ZDC25: Mark Woods, Splunk - Walking the Tightrope: Navigating Risk, Impact and Change.
Blue Team Village·49 min
Karl Lovink
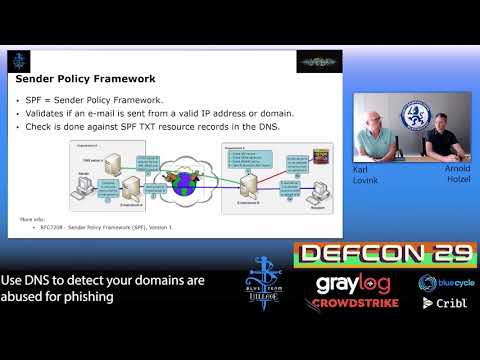
Dutch Tax and Customs investigator Karl Lovink uses DNS telemetry and Splunk to detect fraudulent domains abusing agency brands for phishing in real time.
Cloud Village·26 min
Rod Soto
SIEM tools (Splunk, ELK) for cloud security auditing and threat detection.