Sarah Hume
A battle-tested assumed-compromise methodology for purple teaming that tests detection across the entire killchain.
purple-teamingassumed-compromisekillchain+2
40 talks tagged with this topic.
Loading filters…
1–24 of 40 talks · loading…
Sarah Hume
A battle-tested assumed-compromise methodology for purple teaming that tests detection across the entire killchain.
Black Hat·28 min
Asuka Nakajima
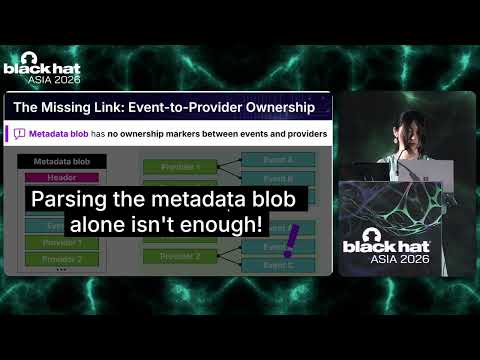
Engineers explore architecture and security mechanisms for Hidden Telemetry: Uncovering TraceLogging ETW Providers You're Not Using (Yet).
Briefings·40 min
Olaf Hartong
What if you could leverage Event Tracing for Windows (ETW) to manipulate telemetry data, challenging the trust placed in endpoint detection and response (EDR) tools.
Car Hacking Village·19 min
Ravi Rajput
Introduces a sequence-learning approach that analyzes inter-signal correlations in raw CAN bus payloads to detect stealthy contextual automotive attacks.
Creator Stage·20 min
Emma Stewart
Separates cyberattacks from physical power dynamics, analyzing grid oscillations, transformer fires, and blackstart scenarios to diagnose grid disturbances.
Creator Stage·26 min
Brandon Bailey
Applies offensive techniques from the SPARTA framework to generate behavioral indicators (IoBs) and design realistic intrusion detection systems for spacecraft.
Creator Stage·21 min
Ben Hawkins
Demonstrates purple team methodologies applied to satellite ground segments and flight software to validate threat detections and improve space cyber defenses.
Packet Hacking Village·1 hr 4 min
Ezz Tahoun
LLM-free alert contextualization and modular correlation pipeline to uncover root causes and attack flows in noisy IoT environments.
PROIDEA Events·21 min
Industry experts analyze emerging threats surrounding PLNOG ONLINE 3: Modern Open Network Telemetry Processing (Avi Freedman).
PROIDEA Events·24 min
Avi Alkobi
Industry experts analyze emerging threats surrounding PLNOG22 - Avi Alkobi - Network Telemetry, Visibility and all in between.
PROIDEA Events·21 min
Jarosław Grabowski
Industry experts analyze emerging threats surrounding PLNOG22 - Jarosław Grabowski - The Age of Enlightenment is Coming, or Telemetry in Networks.
SAINTCON·26 min
Bill Clay III
Security researchers examine technical aspects of 2018 - Bill Clay III - Using metadata and telemetry to detect malware in encrypted traffic.
The Linux Foundation·26 min
Details application-Aware Power Telemetry Collection in “Green Edge” Computing Networks and evaluates key implications for security practitioners.
The Linux Foundation·41 min
Paras Mamgain · Kiran Darbha
Demonstrates effective Observability with Open Telemetry and evaluates key implications for security practitioners.
The Linux Foundation·35 min
Shivay Lamba · Saiyam Pathak
Investigates exploring the Landscape for Open Telemetry for Wasm and evaluates key implications for security practitioners.
The Linux Foundation·51 min
Active Telemetry
Examines LF Live Webinar: Bridging the Dev-SRE Gap with Active Telemetry and evaluates key implications for security practitioners.
The Linux Foundation·19 min
A Comprehensive Benchma... Henrik Rexed
Demonstrates telemetry Showdown: Fluent Bit vs. OpenTelemetry Collector - A Comprehensive Benchma... Henrik Rexed and evaluates key implications for security practitioners.
The Linux Foundation·30 min
Frank Brockners
Evaluates telemetry: Industry Status, Challenges, and OSS Opportunities and evaluates key implications for security practitioners.
The Linux Foundation·38 min
Jesse Sanford · Jagadish Ramidi
Discusses the Telemetry of Trust, Using Attestations to Secure Your SDLC and evaluates key implications for security practitioners.
TROOPERS IT Security Conference·54 min
Engineers explore architecture and security mechanisms for TR19: The Anatomy of Windows Telemetry.
Creator Stage·55 min
E Tahoun · L Hamida
Demonstrates how open-source data science models cluster heterogeneous security alerts to uncover coordinated multi-stage cyber attacks.
Creator Stage·21 min
G Horvath · W Tam
Details the design of a modular wireless survey platform and PacketGlass, an Elasticsearch visualization pipeline processing raw 802.11 PCAP data.
Creator Stage·43 min
Josh Pyorre
Explores building detection signatures from network transaction timing intervals to identify malicious command-and-control communication.
Creator Stage·24 min
Matt Thomassen · Sean McKeever
Analyzes airborne Wi-Fi signal propagation and reconnaissance data collected by warflying a small Cessna aircraft at various altitudes.