Black Hat·59 min
Engineers explore architecture and security mechanisms for Browsers Gone Wild.
browserwildbrowsers
44 talks tagged with this topic.
Loading filters…
1–24 of 43 talks / 44 · loading…
Black Hat·59 min
Engineers explore architecture and security mechanisms for Browsers Gone Wild.
Black Hat·46 min
Engineers explore architecture and security mechanisms for HTTP Cookie Hijacking in the Wild: Security and Privacy Implications.
Black Hat·39 min
a Large Scale Study
Security researchers examine technical aspects of TCP Injection Attacks in the Wild - a Large Scale Study.
BSides Lisbon·26 min
Carlos Friaças
Carlos Friaças details [BSL2023] Internet Hijacks, still in the wild west era.
BSides Lisbon·37 min
Nacho Sorribas
Presenters detail vulnerability discovery and exploitation in 2017 - Wild Wild Web App to Domain Admin: A Case Study by Nacho Sorribas.
CODE BLUE·37 min
Liis Vihul
Analysts investigate attack surfaces and defenses concerning [CB19] Keynote:Cyberspace - A Lawless Wild West or Orderly Chaos? by Liis Vihul.
Ekoparty 2025·37 min
David Carmona
David Carmona analyzes Thermostats Gone Wild: Gaining Domain Admim from an Unsecured HVAC System 🚨.
Ekoparty Security Conference·49 min
Real World exploits · mitigations Johann Rehberger
Evaluates indirect Prompt Injections in the Wild - Real World exploits and mitigations Johann Rehberger and evaluates key implications for security practitioners.
Ekoparty Security Conference·40 min
Marília Rocha
Provides security, Scorpions, AI, Wilds and Coding: The (Un)Expected and evaluates key implications for security practitioners.
FIRST·1 hr
Presenters detail vulnerability discovery and exploitation in Life in Security - Practitioners in the Wild (Panel).
FIRST·24 min
Analysts investigate attack surfaces and defenses concerning Security Advisories and Vulnerability Prioritization in the Wild.
FIRST·53 min
Presenters detail vulnerability discovery and exploitation in Where The Wild Things Are: The State Of Open Source Supply Chain Risk Management In Three Stories.
HITCON·42 min
Security researchers examine technical aspects of Prompt Injections in the Wild - Exploiting Vulnerabilities in LLM Agents | HITCON CMT 2023.
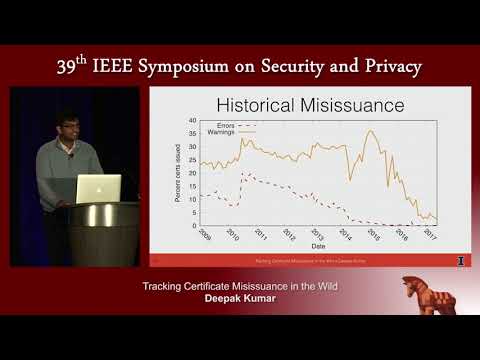
IEEE Symposium on Security and Privacy·18 min
Analysts investigate attack surfaces and defenses concerning Tracking Certificate Misissuance in the Wild.
LayerOne 2025·43 min
Security researchers examine technical aspects of Boo Boo Runs Wild: Guerilla Open-Source Manufacturing (machinist).
nullcon·46 min
Analysts investigate attack surfaces and defenses concerning A UEFI firmware bootkit in the wild by Ivan Kwiatkowski | Nullcon Goa 2022.
OWASP Foundation·41 min
Engineers explore architecture and security mechanisms for Exploitable In The Wild CVE Appears! But Should We Fix 'em All?.
OWASP Foundation·54 min
OWASP AppSec California 2015 analyzes Unicodes Gone Wild - Christien Rioux (DilDog).
PROIDEA Events·44 min
Engineers explore architecture and security mechanisms for PaweŁ Łukaszuk - Deno in the wild.
SEC-T·14 min
Industry experts analyze emerging threats surrounding 0x0A: Calle Svensson - Unauthenticated encryption in the wild.
Security BSides San Francisco·34 min
Details BSidesSF 2016 - A year in the wild: fighting malware at the corporate level (Kuba Sendor) and evaluates key implications for security practitioners.
The Linux Foundation·35 min
Demonstrates FDC3 in the Wild - Real World Use Cases that Help Evolve the Stan... Eugene Sorenson & Robert Friend and evaluates key implications for security practitioners.
The Linux Foundation·19 min
Julien Semaan · Corey McGalliard
Reviews gitOps Gone Wild: Hardening Delivery Pipelines for the AI Era and evaluates key implications for security practitioners.
The Linux Foundation·33 min
Christine Yen
Analyzes leveraging SRE and Observability Techniques for the Wild World of Building on LLMs and evaluates key implications for security practitioners.