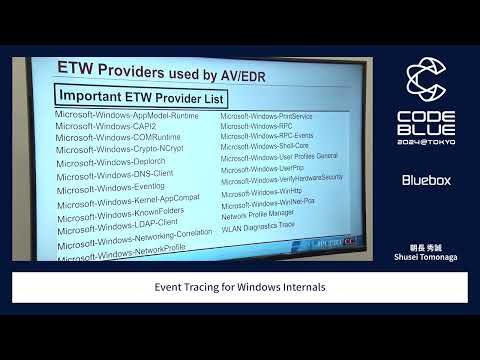
CODE BLUE 2024·44 min
Industry experts analyze emerging threats surrounding [CB24]Event Tracing for Windows Internals.
windowswindows-internalstracing
15 talks tagged with this topic.
Loading filters…
1–15 of 15 talks · loading…
CODE BLUE 2024·44 min
Industry experts analyze emerging threats surrounding [CB24]Event Tracing for Windows Internals.
Main Stage·45 min
RJ McDown
RJ McDown presents Obligato, a covert implant communication framework that abuses legacy Windows session architectures to decouple C2 traffic from malware processes.
Main Stage·40 min
Alessandro Magnosi · Arash Parsa · Athanasios Tserpelis
Introduces Full Moon and Half Moon call stack spoofing techniques to evade EDR inspection, alongside the Eclipse kernel detection algorithm.
Blue Team Village·1 hr
Connor Morley
Connor Morley analyzes Windows in-memory injection techniques—including process hollowing and thread hijacking—and how defenders detect them.
Blue Team Village·50 min
Project Obsidian
Project Obsidian details hunting for malicious scheduled tasks, cron jobs, and stealthy persistence mechanisms across enterprise endpoints.
Main Stage·45 min
Ben Barnea · Ophir Harpaz
Akamai researchers Ben Barnea and Ophir Harpaz explore Microsoft Remote Procedure Call (MS-RPC), discovering zero-day vulnerabilities in core Windows services.
Main Stage·24 min
Omri Misgav
Omri Misgav investigates Bring Your Own Vulnerable Driver (BYOVD) attacks, subverting Windows Driver Signature Enforcement to deploy stealthy kernel rootkits.
Main Stage·42 min
Wietze Beukema
Wietze Beukema presents novel DLL hijacking techniques that manipulate user-controlled environment variables to execute code via signed binaries with zero file drops.
Main Stage·26 min
Tarek Abdelmotaleb · Bramwell Brizendine
Tarek Abdelmotaleb and Dr. Bramwell Brizendine demonstrate weaponizing Windows syscalls into pure position-independent shellcode, evading modern EDR hooks.
SteelCon·24 min
Niharika
Game Cheats Vs Anti-Cheats: A Journey Through Windows Internals.
Main Stage·42 min
Tomer Bar · Eran Segal
SafeBreach researchers analyze five years of Windows CVE patterns to predict recurring vulnerability classes and discover new zero-day local privilege escalations.
Main Stage·39 min
Bill Demirkapi
Bill Demirkapi demystifies writing modern Windows kernel rootkits, demonstrating novel kernel hooking techniques to manipulate user-mode network stacks.
Main Stage·31 min
Bill Demirkapi
Bill Demirkapi answers community questions regarding modern Windows kernel development, PatchGuard interactions, and network driver hooks.
Main Track 1·20 min
Dor Azouri
Exploiting Windows BITS service state files to inject jobs and execute code as NT AUTHORITY/SYSTEM.
Main Stage·18 min
Christopher Campbell
Christopher Campbell explores the $env:path less traveled at DEF CON 22, examining powershell and practical defenses.


