SQL Injection
Kevin Spett explores sql injection at DEF CON 10, examining sql-injection and practical defenses.
Summary
Architecture and Background
Kevin Spett - SQL Injection SQL injection is a technique for exploiting web applications that use client-supplied data in SQL queries without stripping potentially harmful characters first.
Vulnerability Analysis
Despite being remarkably simple to protect against, there is an astonishing number of production systems connected to the Internet that are vulnerable to this type of attack.
Exploitation and Demonstrations
The objective of this talk is to educate the professional security community on the techniques that can be used to take advantage of a web application that is vulnerable to SQL injection, and to make clear the correct mechanisms that should be put in place to protect against SQL injection and input validation problems in general.
Remediation and Defensive Strategies
Kevin Spett is a web application security expert and researcher. His discovery new SQL injection attack techniques and frequent security mailing list postings have made him among the most respected web application security professionals in the world. Kevin's responsibilities include maintaining the SPI Dynamics SecureBase and researching web application security concepts and software. He has been a SPI Dynamics employee since its inception.
Related talks

Main Stage·34 min
Jason A. Novak · Andrea London
Jason A. Novak and Andrea London details copy of the slides for this talk are here: Extras: SQL ReInjector - Automated Exfiltrated Data Identification Jason A.

Main Stage·21 min
Nick Galbreath
Nick Galbreath details copy of the slides for this talk are here: New Techniques in SQLi Obfuscation: SQL never before used in SQLi Nick Galbreath SQLi remains a popular sport in the security arms-race.
Main Stage·44 min
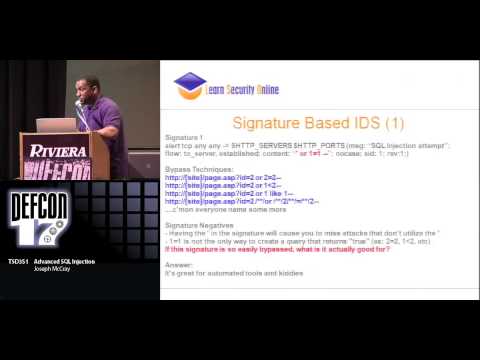
Joseph McCray
Joseph McCray explores advanced sql injection at DEF CON 17, examining sql-injection and practical defenses.